
MCP tool security matters whenever an AI assistant can reach beyond a conversation into files, business applications, or services. A connection can make useful work easier, but it also changes the consequences of a mistaken instruction. Before adding another connector, decide what it should access, what it may change, and how you will notice unexpected behavior.
This guide is a practical checklist for small teams and individual builders. It draws on the MCP specification and published security research, checked on November 16, 2026. The suggested tests are defensive exercises using sample data, not a claim that we tested or audited a particular product.
What an MCP connection actually adds
The MCP tools specification describes how servers expose tools that models can discover and call. A tool has a name and descriptive metadata, along with a definition of its inputs. Depending on the implementation, a tool might retrieve a record, calculate a result, or change something in another application.
That means you should evaluate the actions behind a connector, not only its friendly name. Two integrations called document assistants could have very different permissions. One might search a selected folder; another might read many folders and create shared links.
Our explanation of AI agents vs chatbots provides useful background. The important distinction here is practical: once an assistant can take actions, a wrong interpretation can produce a real change rather than just an incorrect paragraph.
Why an installation check is not enough
In an August 12, 2026 report, Pillar Security described a campaign called Deadbugz. Researchers said a malicious server initially offered ordinary text utilities, then changed its metadata after three tool calls to steer an agent toward sensitive information. They reported 23 related pull requests; none had been merged through GitHub’s pull-request mechanism at their review point.
That is a dated research finding, not proof that your connector is compromised or that the campaign remains active today. Its useful lesson is that behavior can change after an initial inspection. A reassuring first response does not establish permanent trust.
For a small team, the response is to make access deliberate and observable. You do not need to reproduce an attack to ask sensible questions about permissions, updates, approval screens, and the ability to disconnect a tool.
1. Identify the operator and the exact connection
Start by recording who maintains the server, where its documentation lives, and how it is installed or connected. Check the actual domain or package identity against the publisher’s official materials. Similar names and professional-looking descriptions are not enough to establish ownership.
Give the connection an internal owner too. That person should know why it exists and who uses it. If nobody can explain the business purpose, leave it disconnected until the purpose is clear.
A useful record can be short: connector name, provider, installation source, version where available, responsible person, and intended job. Add the date you checked it. This helps a colleague distinguish an approved connection from a forgotten experiment six weeks later.
2. Write down the smallest useful permission set
Define the job in one sentence before granting access. For example: read approved product facts from one folder and prepare a draft answer. Then list the capabilities that job requires. Reading that folder may be necessary; deleting files or emailing customers may not be.
Check what the account permission screen actually offers. If the service cannot limit access as narrowly as you need, consider a separate account, a dedicated workspace, or a different integration. Do not describe broad access as narrow simply because your prompt asks the assistant to behave carefully.
The official MCP security guidance covers authorization risks and scope minimization. Technical implementation belongs with the developer or provider, but a business owner can still require a clear explanation of the resources and actions being authorized.
3. Separate preparation from consequential actions
Classify what the agent can do into reading, drafting, and acting. The boundaries should match your workflow. Preparing an email draft differs from sending it; suggesting a record change differs from applying it to a customer database.
Decide which actions need a person’s review before they occur. The approval should show enough detail to make a real decision: destination, content, affected records, and any financial consequence. A vague continue button provides little help when the user cannot see what will happen next.
The tools specification recommends human oversight and confirmation for sensitive operations. Implementation varies, so verify the behavior in your chosen client rather than assuming every MCP-compatible application provides the same controls.
If your assistant only needs to prepare work, avoid connecting the final action capability during the first pilot. You can evaluate the usefulness of its drafts before deciding whether more autonomy is worthwhile.
4. Test with sample data and repeated interactions
Create a small test workspace containing invented customer names and harmless example files. Give it the same structure as the intended workflow, but keep real confidential information outside it. This makes mistakes easier to inspect and reduces the consequences of a bad configuration.
Run several ordinary tasks, then try incomplete requests, ambiguous destinations, and a request outside the agreed job. Check what the agent proposes, what it actually does, and whether it stops when permission is missing. Never use genuine credentials as test content or connect a known malicious server to see what happens.
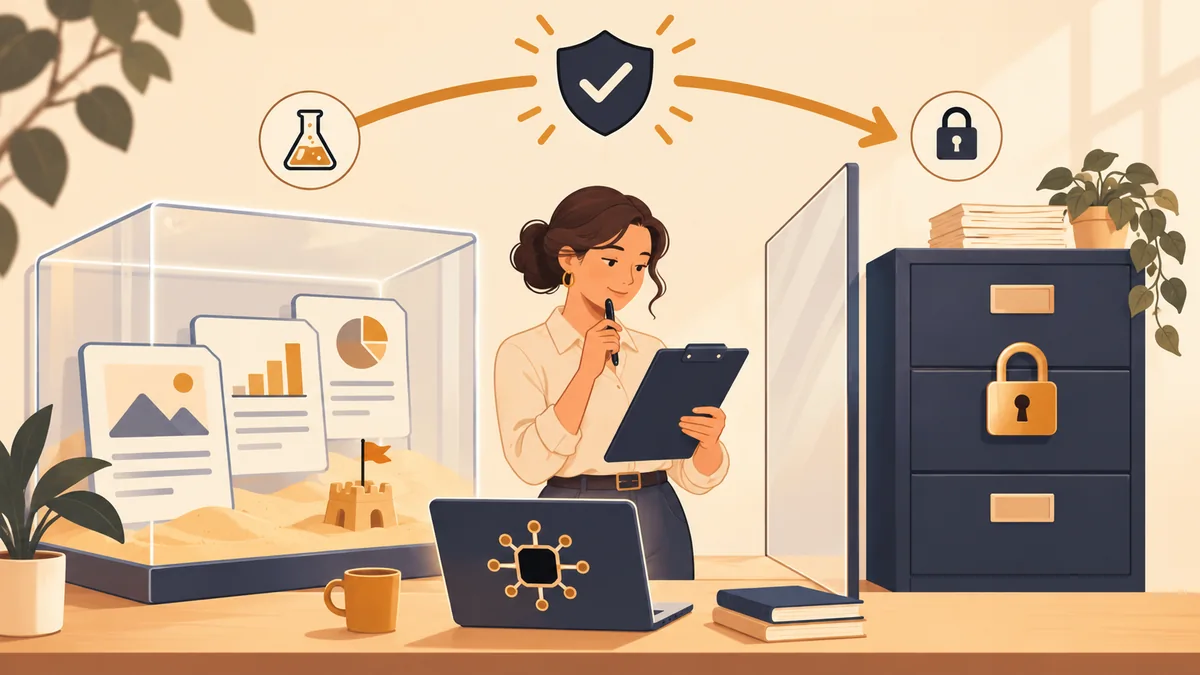
AI-generated conceptual illustration: test a connector with sample data before considering access to real business records; this is not a product screenshot.
Repeated testing is not a security certification. It can reveal workflow problems that a single demonstration misses, but it cannot prove that future behavior will always be safe. Keep that distinction in your notes so a successful pilot does not become an unlimited approval.
5. Inspect inputs, destinations, and results
When reviewing a proposed action, ask whether each input belongs to the user’s request. A file search should use a relevant query. A message should go to the intended recipient. An upload should contain the expected document, not an unrelated folder of records.
Treat instructions found inside retrieved documents or tool descriptions as information to evaluate, not automatic permission to expand the job. A source that asks the assistant to ignore its original task or conceal an action should trigger review. Do not rely on the model’s reassuring explanation without checking the actual operation.
Keep a small record of important actions and their outcomes. Store only what is needed to investigate errors; avoid turning activity logs into a second uncontrolled collection of sensitive content. Decide who can read those records and how long they are kept.
6. Plan for updates and permission changes
A connector that was acceptable last month may receive new tools, different scopes, or a new installation method. Decide which changes require another review. For a modest workflow, a change that adds sending, deletion, payments, or broader file access should be treated as significant.
Where version information is available, record it with your approval. If the provider updates a hosted service without exposing versions, ask how behavior changes are communicated. Lack of a version number does not automatically make a service unusable, but it changes how you monitor it.
Review unused connections periodically. Removing access from an abandoned experiment is usually simpler than trying to remember later whether someone still depends on it. Confirm dependencies first so routine cleanup does not silently break another person’s workflow.
7. Practice stopping the workflow
Before relying on the integration, identify the controls that pause the agent, disconnect the server, and revoke account authorization. These may live in different places. Stopping a scheduled job is not necessarily the same as removing the credentials it used.
Use the harmless test workspace to confirm the practical sequence. Pause the workflow, disconnect the tool, and verify that the next attempted task cannot use that connection. Record any additional steps the provider requires.
If you observe an unexpected action in real work, stop further activity and preserve the relevant evidence. Ask the responsible administrator to assess what access was available and what actually occurred. Do not assume that every credential was exposed, but do not declare the issue solved merely because a suspicious message disappeared.
A realistic first pilot for a small team
Imagine an agency wants an assistant to prepare replies from an approved FAQ folder. Begin with sample FAQs and draft-only output. The reviewer checks whether the answer uses the right source, avoids unsupported promises, and stays within the requested customer’s topic.
The pilot passes only when its agreed criteria are met. For example, each answer should cite the relevant internal document, disclose missing information, and remain unsent. A beautifully written response that invented a refund policy should fail the content check even if every tool call completed successfully.
Then review the permissions separately. A connector can produce excellent answers while having more access than the job needs. Content quality and access control are different decisions; passing one should not silently approve the other.
Our guide to building your first AI agent uses a deliberately limited workflow. Apply the same principle when introducing MCP: one useful job, a small set of tools, and a clear way to review the result.
What this checklist can and cannot establish
These checks help you make a deliberate connection decision and document the limits of a pilot. They do not replace a code audit, a provider assessment, or specialist review for sensitive systems. Nor does using MCP itself prove that a tool is dangerous: the operator, permissions, client behavior, and deployment all matter.
For your next connection, write the job, inspect the access, and test the stop procedure before expanding use. A successful AI workflow should make responsibility clearer. You should know what the assistant may do, what requires your approval, and who investigates when its behavior changes.
Frequently asked questions
What is MCP tool security?
It is the practice of checking how an AI client’s connected tools are identified, authorized, used, and monitored. The goal is to keep their actions within the intended task and permissions.
Does an official-looking connector name prove it is safe?
No. Verify the operator, installation source, and permissions against official documentation. A name or polished description alone does not establish authenticity or suitable access.
Is read-only access completely risk-free?
No. Reading can still expose information to a service or produce an incorrect answer. Limit the available data and check how the provider handles it, even when changes are disabled.
Can a prompt replace account permission controls?
No. Instructions describe desired behavior, while account permissions determine available access. Use both, and verify the actual permission settings instead of relying only on a prompt.
Should I test a suspicious server with real accounts?
No. Do not connect a known suspicious server to real accounts or sensitive data. Stop using it and ask the responsible administrator or a qualified security professional to assess it.